Define the contents of a customer identity verification bundles archive
An onboarding analyst needs to review a customer identity packet and escalate one mismatched field to a supervisor without distributing the complete document set. Before discussing encryption, list what the project actually produces. For identity-review teams, onboarding operations and small verification providers, the records can include proof-of-address documents, ID images, verification notes, exception approvals and case reference IDs. Different types may deserve different recipients and retention rules.
Create a data inventory
Enumerate proof-of-address documents, ID images, verification notes, exception approvals and case reference IDs. For every type, note whether it contains direct identifiers, whether the document must remain editable, and whether it has an authoritative owner. Do not upload real example files to a public test service.
Define record boundaries
Use a case or project identifier in filenames while keeping the identity mapping in its own controlled location. The customer identity verification bundles archive should not silently include every download made during the work; temporary references and personal files should be excluded unless their purpose is documented.
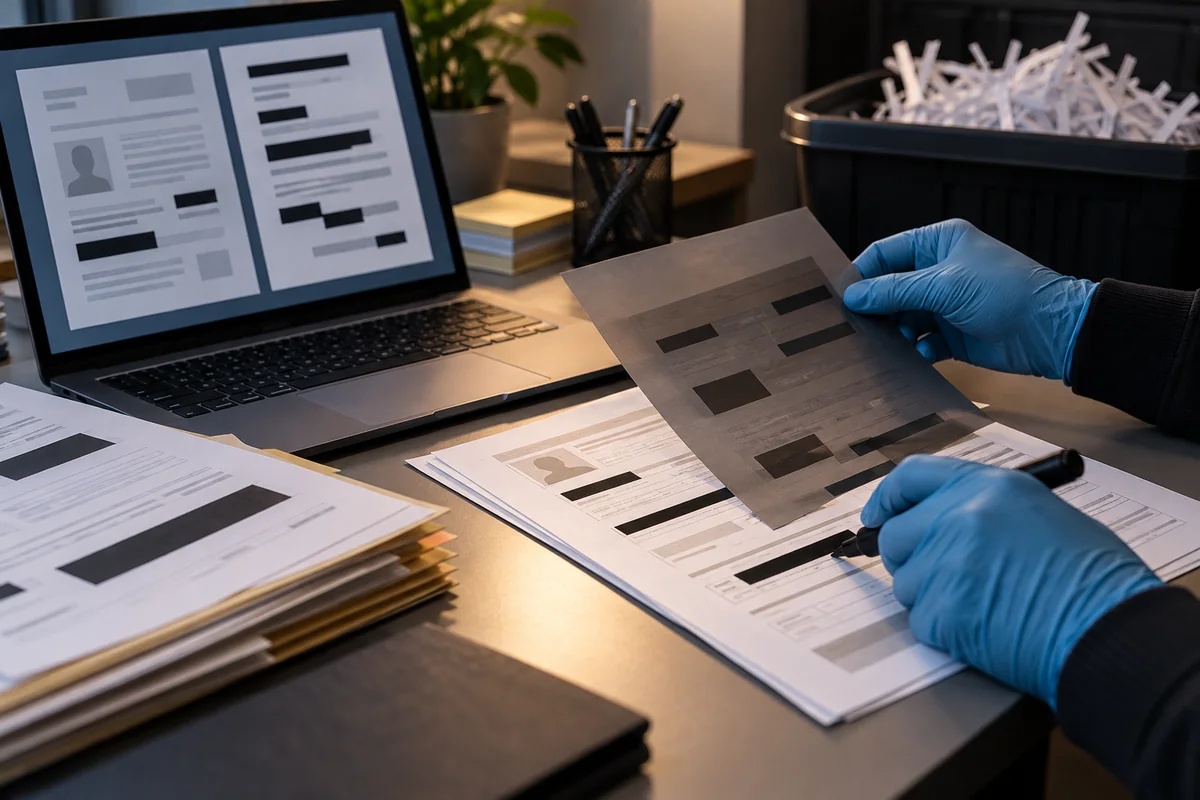
Accept or reject checklist
Keep a record only if it advances one of the documented activities: customer intake, review and escalation, approval decision and retention and destruction. Flag exceptions for the authorized verification reviewer and the case supervisor and make a written decision about versions that conflict.
Sample inventory entry: proof-of-address documents — owner: the authorized verification reviewer and the case supervisor; purpose: customer intake; recipient: named and approved; retention: policy reference required.
Practical implementation checklist
- Identify the accountable approver for customer identity verification bundles and write down the exact event being protected.
- Choose a non-sensitive sample drawn from the same format as exception approvals; never use a real identity, key or patient record in a public example.
- Compare the unprotected working copy, restricted recipient copy and intended retained copy. Confirm where extra versions are created.
- Record the approved destination, any failed test, and a date for reassessing the workflow when personnel or software changes.
Questions readers should resolve
Should every file related to customer identity verification bundles be retained?
No. Preserve what is required for the documented work and applicable retention obligations; exclude unrelated, duplicated or unsupported material. For customer verification packets, this means checking ID image attachments, handling case reference keys separately, and using a synthetic identity packet as the review example. The acceptance ledger should name who entered the record, whether the identifying field is necessary, and which official retention rule applies.
Who should approve this customer identity verification bundles workflow?
Assign a named owner. In this context, start with the authorized verification reviewer and the case supervisor and confirm the applicable organizational authority.
Research and documentation
These sources support the technical boundaries described here. They are not substitutes for testing the current software on the target device, checking legal requirements, or independently confirming product claims.
Editorial note: No paid link placement is required for this guide. Product information, if mentioned, describes one possible tool and should not be read as an endorsement or an assertion of universal compatibility.